
Solidus Secure
Cybersecurity for industrial products and OT systems
IEC 62443, the Cyber Resilience Act and NIS2 for manufacturing and automation — from risk analysis to implementable security architecture.
- ISA/IEC 62443 (IC32)
- ISO/IEC 27001 Lead Auditor
- INL ICS-300/401
- 11 OT audits (energy sector, as proof of method)
Your product and your plant are now regulated at the same time
For industrial companies, several obligations land together. As a manufacturer you fall under the Cyber Resilience Act (CRA): its reporting obligations have applied since 11 September 2026, and from 11 December 2027 cybersecurity becomes a precondition for CE marking — without conformity, a product cannot be placed on the EU market. At the same time, your customers increasingly ask for evidence against IEC 62443. And as the operator of your own production, NIS2 adds a third layer, with accountability resting on management. We bring these demands into order and turn them into one implementable architecture — instead of three separate projects.
Check your CRA readiness →Services
IEC 62443 – Assessment & Security Architecture
The technical core. We assess your plant or product against the standard, map it to protection levels and derive an implementable architecture.
Learn more →Product Security & CRA
Guidance for manufacturers of products with digital elements through the Cyber Resilience Act — from classification through vulnerability and reporting processes to technical documentation.
Learn more →OT Security Assessment
A security assessment of the operated environment: asset inventory, network segmentation and vulnerability assessment — without disrupting live operations.
Learn more →NIS2 & ISO/IEC 27001
The organisational layer: scoping, risk management and evidence towards the authorities.
Learn more →vCISO & Ongoing Advisory
Security leadership on a retainer, where a dedicated in-house role is not justified.
Learn more →Why Solidus Secure
Engineer, developer and auditor in one person.
An engineering background, more than ten years in software development and experience in financial leadership — we judge security technically, architecturally and commercially, not only against a regulation.
From requirement to implementable architecture.
We do not stop at the report. Risk analysis and the standards (IEC 62443, CRA, NIS2) become concrete architecture and processes that hold up on the plant floor and in product development.
Specialist, not generalist.
A deliberate focus on industrial product and OT security, evidenced by ISA/IEC 62443 (IC32), the ISO/IEC 27001 Lead Auditor qualification and 11 OT audits in the energy sector.
The same method — applied to your sector
Evidence, not promises
In European industrial B2B, evidence counts. So qualifications, a repeatable assessment method and documented audits come first — not marketing claims.
62443
ISA/IEC (IC32)
27001
Lead Auditor
11
OT audits
< 24 h
Response time
How we work
- Step 1
Intro call
free, 30 minutes.
- Step 2
Assessment
current state against IEC 62443, CRA or NIS2.
- Step 3
Action plan
ordered by risk and effort.
- Step 4
Implementation & architecture
ongoing as a vCISO if you wish.
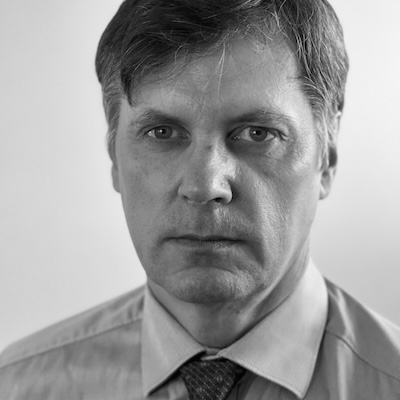
One accountable point of contact
Solidus Secure is led by Vaidas Jokubauskas, with an unusual path across engineering, software development and financial leadership. That combination explains risk in a way that is understood both in the boardroom and on the plant floor.
More about us →Common questions on product, OT and IEC 62443 security
Let's clarify your next obligation — in 30 minutes
A free intro call, no commitment, a reply within 24 hours.